
First, what is AlienVault?
The VirusTotal contact for AlienVault is the support address of the Open Threat Exchange (OTX), at otx.alienvault.com. LevelBlue's documentation describes OTX as an open threat intelligence community. Members share indicators such as IP addresses, domains and file hashes, and a pulse is a group of those indicators reported by the community.
The old alienvault.com addresses now redirect to AT&T Cybersecurity and LevelBlue pages. A domain can land in OTX because a community member put it in a pulse, so your site can be listed without any scan of its content.
Who can't reach you right now
Where it's used, and who shares it
These engines are independent from AlienVault. If they flag you too, each one needs its own request:
 Google Safe Browsing →
 Kaspersky →
 ESET →
 Bitdefender →
How to tell if you're flagged
 VirusTotal. Scan the URL and read the row named AlienVault. The same scan shows what other engines say.
- OTX at otx.alienvault.com. The page has a Search OTX box, plus Browse, Scan Endpoints, Create Pulse, Submit Sample and API Integration menus. Search your domain there to see the pulses that list it. Signing up asks for a username, email, country, password and a consent box, and the page says the OTX account is separate from the LevelBlue Community and legacy Open Threat Exchange accounts.
- User reports. Ask affected users for the warning they see and the address they opened.
Asking AlienVault to fix it
Find the AlienVault row on VirusTotal
Open virustotal.com, pick the URL tab and paste your address. Find the AlienVault row, write down the verdict and copy the report link. No account is needed. If you can, also search the domain on OTX and note the names of the pulses that list it.
Check that it is a mistake
Look for signs that someone abused your site: pages you did not create, unknown redirects, mail sent from your domain that you did not send. If the site was hacked in the past, the listing can be a true record of that. Clean the site first, then write.
Send the email
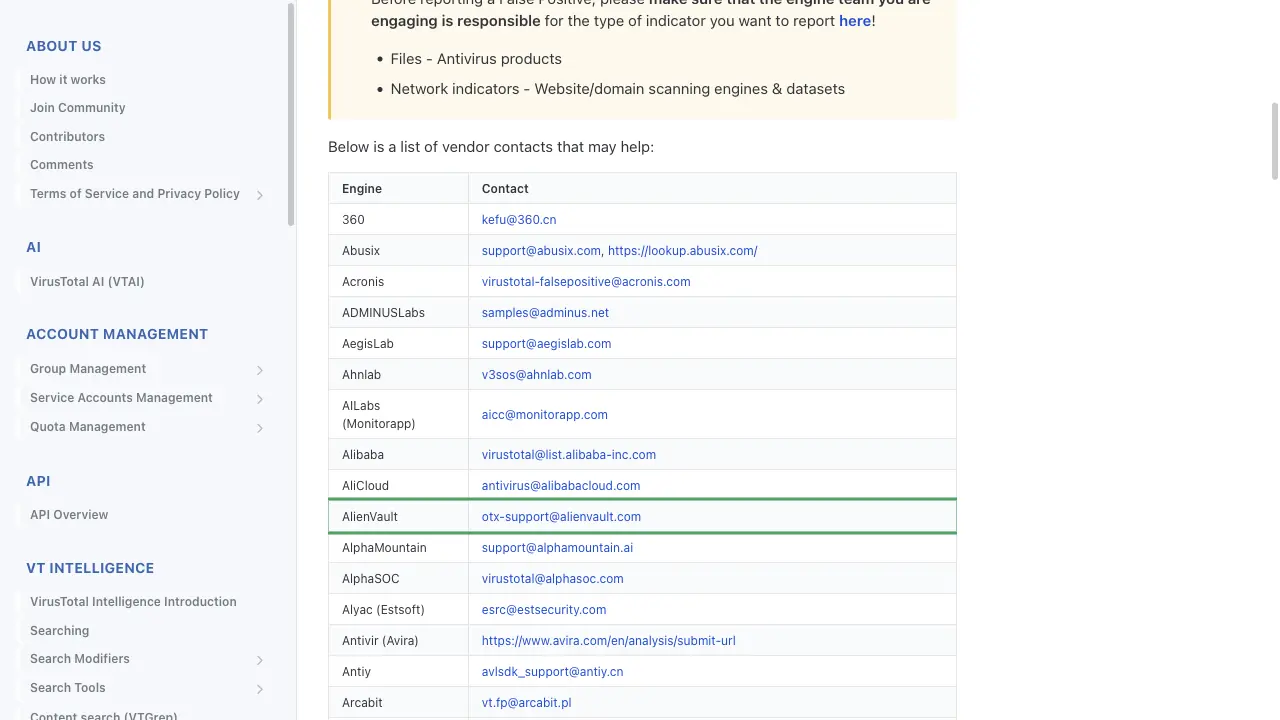
We found no web form for website owners on the AlienVault, AT&T Cybersecurity or LevelBlue pages we opened. The address comes from VirusTotal's list of vendor contacts at docs.virustotal.com/docs/false-positive-contacts. Write to [email protected]. You need no account, and any email address works, so a company address is not required. Include the full URL, the VirusTotal report link, the pulse names if you found them, who owns the site and what it does.
To:      otx-support[at]alienvault[.]com
Subject: False positive: example[.]com flagged as phishing by AlienVault

Hello,

AlienVault flags hxxps://example[.]com as phishing in this VirusTotal report:
hxxps://www[.]virustotal[.]com/gui/url/<id>

I own the domain. It is the website of a family-run bakery in Porto,
with a menu, opening hours and an order form at
hxxps://example[.]com/order that asks only for a name and a phone number.
The site offers no downloads.

Please check the entry and remove it if it is a mistake.

Thank you,
Name
Wait, then reanalyse
The pages we read state no turnaround, so we give none. Later, open your VirusTotal report and click Reanalyze, then look at the AlienVault row. If it has not changed, write again in the same thread.
Other ways to report
AlienVault explains its own rules for false positives on these pages: