First, what is ArcSight Threat Intelligence?
ArcSight Threat Intelligence is the name VirusTotal uses for one of its scanning engines. The contact address VirusTotal gives for this row sits on the opentext.com domain, so we write to OpenText.
OpenText's own pages that we opened do not describe how the ArcSight row reaches its verdict, and they do not say which products read it. OpenText also runs a separate service, OpenText Threat Intelligence (BrightCloud), with a public URL lookup. We could not confirm that this service feeds the ArcSight row.
Who can't reach you right now
Where it's used, and who shares it
These engines are independent from ArcSight Threat Intelligence. If they flag you too, each one needs its own request:
 Google Safe Browsing →
 Kaspersky →
 ESET →
 Bitdefender →
How to tell if you're flagged
 VirusTotal. Scan the URL and look for the ArcSight Threat Intelligence row. It shows the verdict held for your site, and the same scan shows whether other engines flag you too.
 OpenText Threat Intelligence URL or IP lookup. It shows the web category, the reputation score and basic WhoIs data for a URL. It is OpenText's own tool, and we could not confirm that it reflects the ArcSight row, so treat it as a second opinion.
- User reports. Ask affected users for a screenshot of the warning they see.
Asking OpenText to fix it
Find the ArcSight row on VirusTotal
Open virustotal.com, choose the URL tab and paste the full address of your page. Look for the ArcSight Threat Intelligence row and note its verdict. Copy the link of the report from your browser, because the email needs it. No account is needed.
Check that it is a mistake
Scan your server for injected code, check every script you load from another site, and review each page that asks visitors for a password or payment details. Fix anything you find first. Write to OpenText only when the site is clean.
Send the email
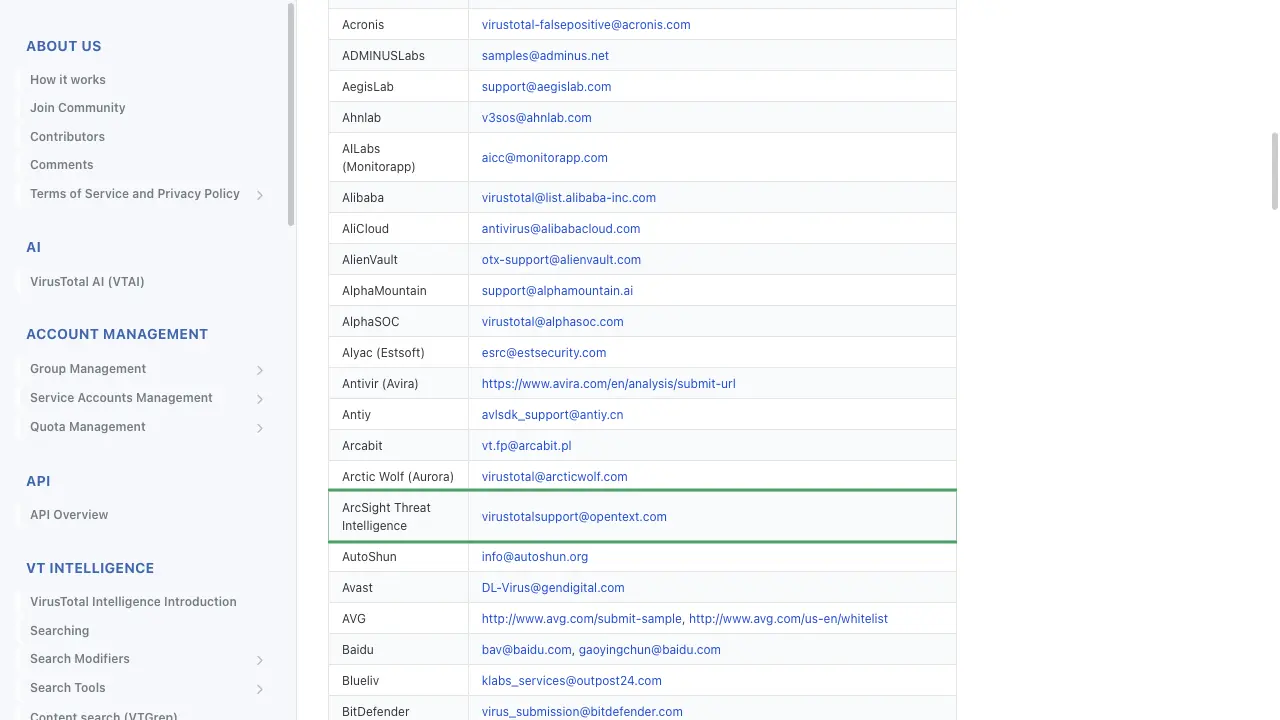
The address comes from VirusTotal's list of vendor contacts at docs.virustotal.com/docs/false-positive-contacts, and we found no web form for the ArcSight row on the OpenText site. Write to [email protected]. You need no account, and any email address works, so a company address is not required. Put the full URL, the VirusTotal report link, the name of the site owner and a sentence about what the site does in the body.
To:      virustotalsupport[at]opentext[.]com
Subject: False positive: hxxps://example[.]com flagged as malicious by ArcSight Threat Intelligence

Hello,

The website hxxps://example[.]com is flagged by ArcSight Threat Intelligence on VirusTotal.
VirusTotal report: hxxps://www[.]virustotal[.]com/gui/url/<id>

The site belongs to Example Ltd, and we own the domain. It is the booking
site for our dance studio. The only form is the contact form at
hxxps://example[.]com/contact, and it asks for a name and an email address.
The site offers nothing to download.

Please review the verdict and remove the detection.

Thank you,
Name
Wait, then reanalyse
OpenText states no turnaround for this address, so we give none. After a while, open your VirusTotal report and click Reanalyze. The ArcSight row shows the verdict it holds now. If nothing changes, write again in the same email thread.
Other ways to report
ArcSight Threat Intelligence explains its own rules for false positives on these pages: