First, what is Rising?
Rising (Beijing Rising Network Security) is a Chinese antivirus vendor. VirusTotal lists it as one of its scanning engines, and a Rising verdict shows up as its own row in the VirusTotal report.
Rising runs a security forum at bbs.rising.com.cn. Its section for suspicious files takes false positive reports for files and websites, and members of the Rising development team answer them in the thread.
Who can't reach you right now
Where it's used, and who shares it
These engines are independent from Rising. If they flag you too, each one needs its own request:
 Google Safe Browsing →
 Kaspersky →
 ESET →
 Bitdefender →
How to tell if you're flagged
 VirusTotal. Scan the URL and look for the Rising row. It shows the verdict Rising holds for your site, and the same scan shows whether other engines flag you too.
 The Rising forum section 可疑文件交流 (suspicious file exchange). Other site owners post their false positive reports there, so you can see how Rising answers.
- User reports. Ask affected users for a screenshot of the warning and the virus name from the Rising log.
Asking Rising to fix it
Find the Rising row on VirusTotal
Open virustotal.com, choose the URL tab and paste the full address of your page. Look for the Rising row and note its verdict. Copy the link of the report from your browser, because your forum post needs it. Scan both the address with www and the one without if visitors use both.
Check that it is a mistake
Scan your server and your third-party scripts for injected code, and look at every page that asks visitors for a password or payment details. Fix anything you find first. Post to Rising only when the site is clean.
Create a forum account
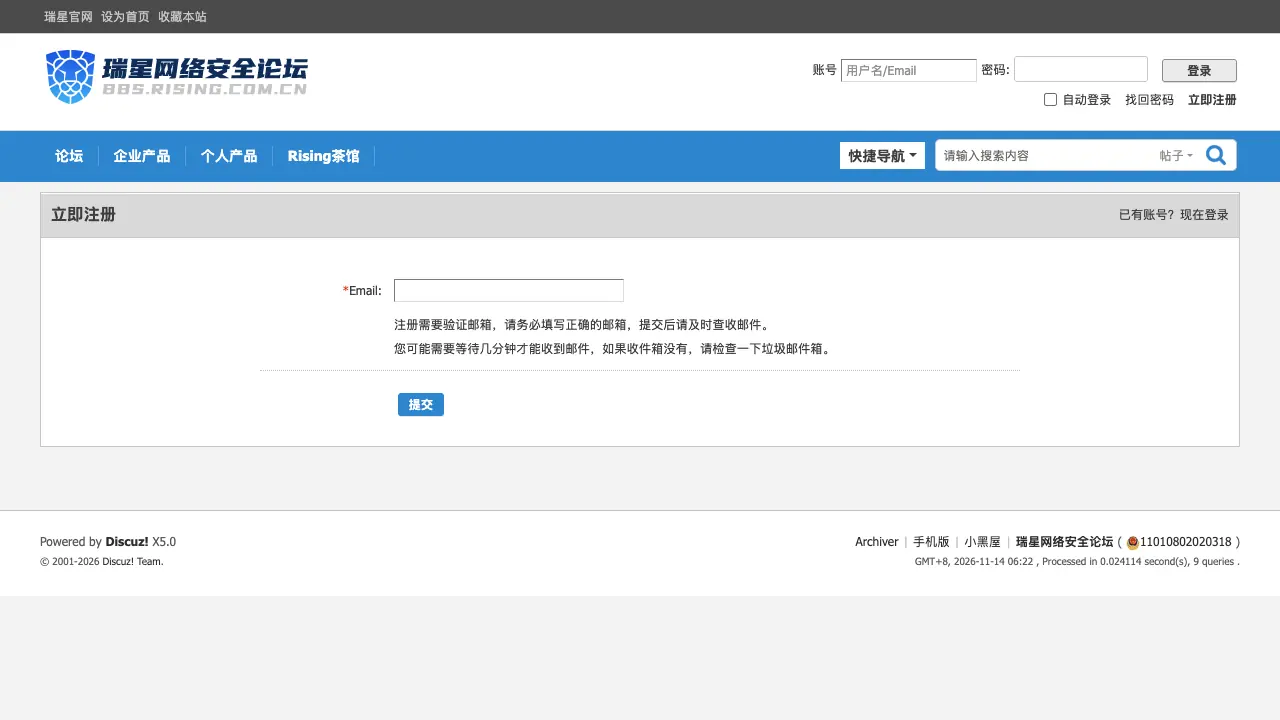
Open the sign-up page at bbs.rising.com.cn/member.php?mod=register (立即注册, register now). The form asks only for an Email, and Rising sends a link to confirm it. The page says the email can take a few minutes and can land in the spam folder. Agree to the forum terms (同意). The form asks for no phone number, no company name and no company email, so a personal address works.
Post a false positive thread
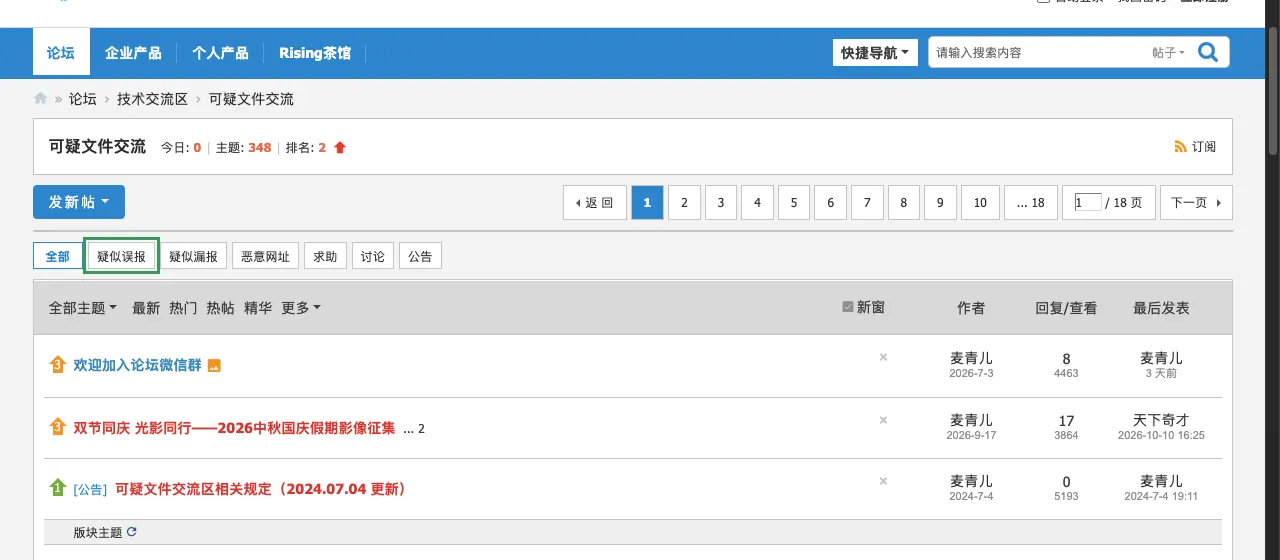
Sign in and open the section 可疑文件交流. Click 发新帖 (new thread) and set the thread type to 疑似误报 (suspected false positive). Put the domain and the verdict in the title. In the body give the full URL, the VirusTotal report link, who owns the site and what it does, and offer to prove ownership, for example with a file on the site. A phishing flag on a website has no file to attach. The forum is in Chinese, and in the threads we read an English post got its answer in English. VirusTotal's list of vendor contacts also gives [email protected], but the replies we saw came in the forum.
Section:      可疑文件交流 (suspicious file exchange)
Thread type:  疑似误报 (suspected false positive)
Title:        False positive: example[.]com flagged as phishing
Body:         Hello,
              I own example[.]com. Rising flags hxxps://example[.]com/
              as phishing on VirusTotal. This is a false positive.
              VirusTotal: hxxps://www[.]virustotal[.]com/gui/url/<id>
              The site is the online shop of Example Ltd. The only
              form is the customer login, and it sends data to our
              own server. The site offers nothing to download.
              I can confirm ownership of the domain, for example with
              a file on the site. Please review the verdict.
              Thank you,
              Name
Report a file
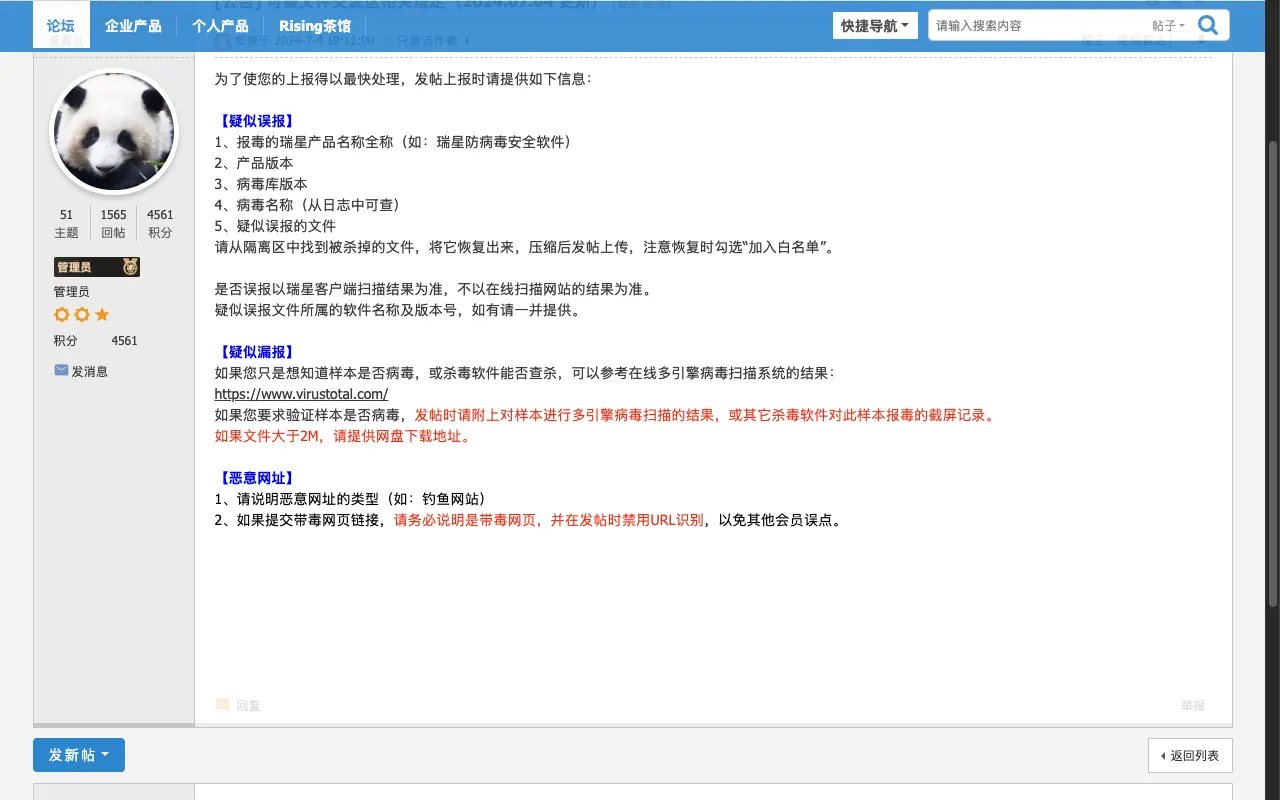
Use the same section and thread type. The section rules ask for five things: the full name of the Rising product, the product version, the virus database version, the virus name from the log, and the file. Restore the file from quarantine (隔离区) with the box 加入白名单 (add to whitelist) ticked, compress it and attach it to the post. Add the name and version of the software the file belongs to. The rules say Rising judges a file false positive by the result of the Rising client, not by online scanning sites.
Thread type:  疑似误报 (suspected false positive)
Title:        False positive: example-app-setup.exe
Body:         1. Product: <full name of your Rising product>
              2. Product version: <version>
              3. Virus database version: <version>
              4. Virus name: <name from the Rising log>
              5. File: example-app-setup.zip (attached)
              Software: Example App 2.1, from
              hxxps://example[.]com/download
Wait, then rescan
Rising states no turnaround, so we give none. In the website threads we read, a member of the Rising development team (开发团队) replied in the thread that the domain was whitelisted and asked the poster to rescan on VirusTotal. When you get that reply, open your VirusTotal report and click Reanalyze. The Rising row shows the verdict it holds now.
Other ways to report
Rising explains its own rules for false positives on these pages: